Authorisation
Build an OAuth server, add mTLS, PAR, DPoP and PS256 signing, then prove the profile holds.
finXFAPI 2.0 pre-built and tested, with CSR, key rotation and JWKS hosting automated.
Secure, consent-driven APIs for partners and customers, running inside your own data centre or private cloud, in front of your core rather than inside it. Security, consent and data control are built in.
What is in the box
From a multi-year build to a first release in weeks
Why finX
Open finance is easy to announce and hard to run securely at scale. None of this differentiates your bank, and all of it sits between you and your first partner.
| Capability | Built in-house | With finX |
|---|---|---|
| Authorisation | Build an OAuth server, add mTLS, PAR, DPoP and PS256 signing, then prove the profile holds. | FAPI 2.0 pre-built and tested, with CSR, key rotation and JWKS hosting automated. |
| Consent | Schema, approval screens, grant, renew and revoke, plus an audit trail a regulator accepts. | Turnkey consent engine with published approval screens and an immutable audit trail. |
| Core mapping | An adapter per endpoint, maintained through every core release. | Camel route templates and SDKs, mapped once, low-code, by your own architects. |
| Partner testing | A sandbox, mock data and a test suite before you will expose production. | Partner sandbox with OpenAPI specs, mock data and a full FAPI 2.0 test suite. |
| Staying current | Rework every time the standard or a partner's needs change. | A mapping change and a test re-run, because schema is configuration. |
Architecture
Partners, customers and regulators connect at the edge, secured end to end with FAPI 2.0. finX does not replace your core, identity provider or API gateway.
Scroll the diagram sideways →
Production-ready, deployed your way
How it works
Every step is secured with FAPI 2.0. Customers can revoke consent at any time, and every access is recorded.
The customer asks a partner app to share their account data.
CustomerThe partner calls finX over mTLS with DPoP-bound tokens.
PartnerA pushed authorisation request starts the consent flow.
finXThe customer approves or denies on your consent screen.
CustomerThe active consent scope is checked on every call.
finXBank data is fetched and mapped to the agreed schema.
BankA signed, encrypted response goes back to the partner.
finXProduct preview
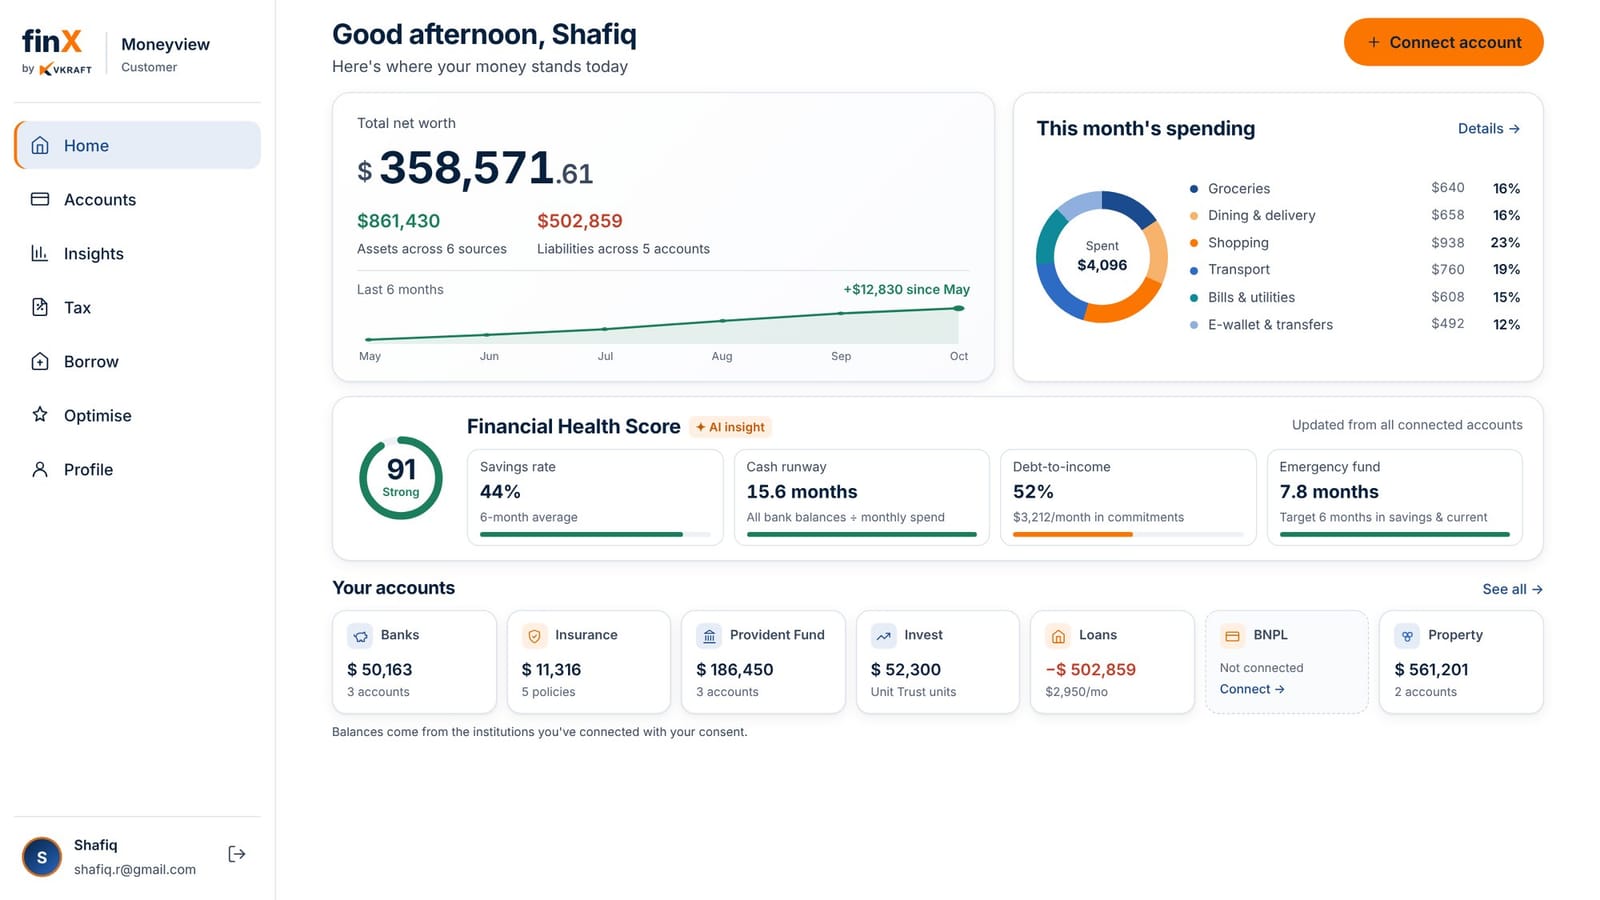
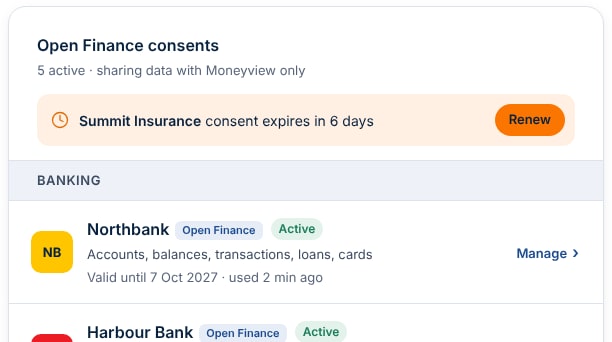
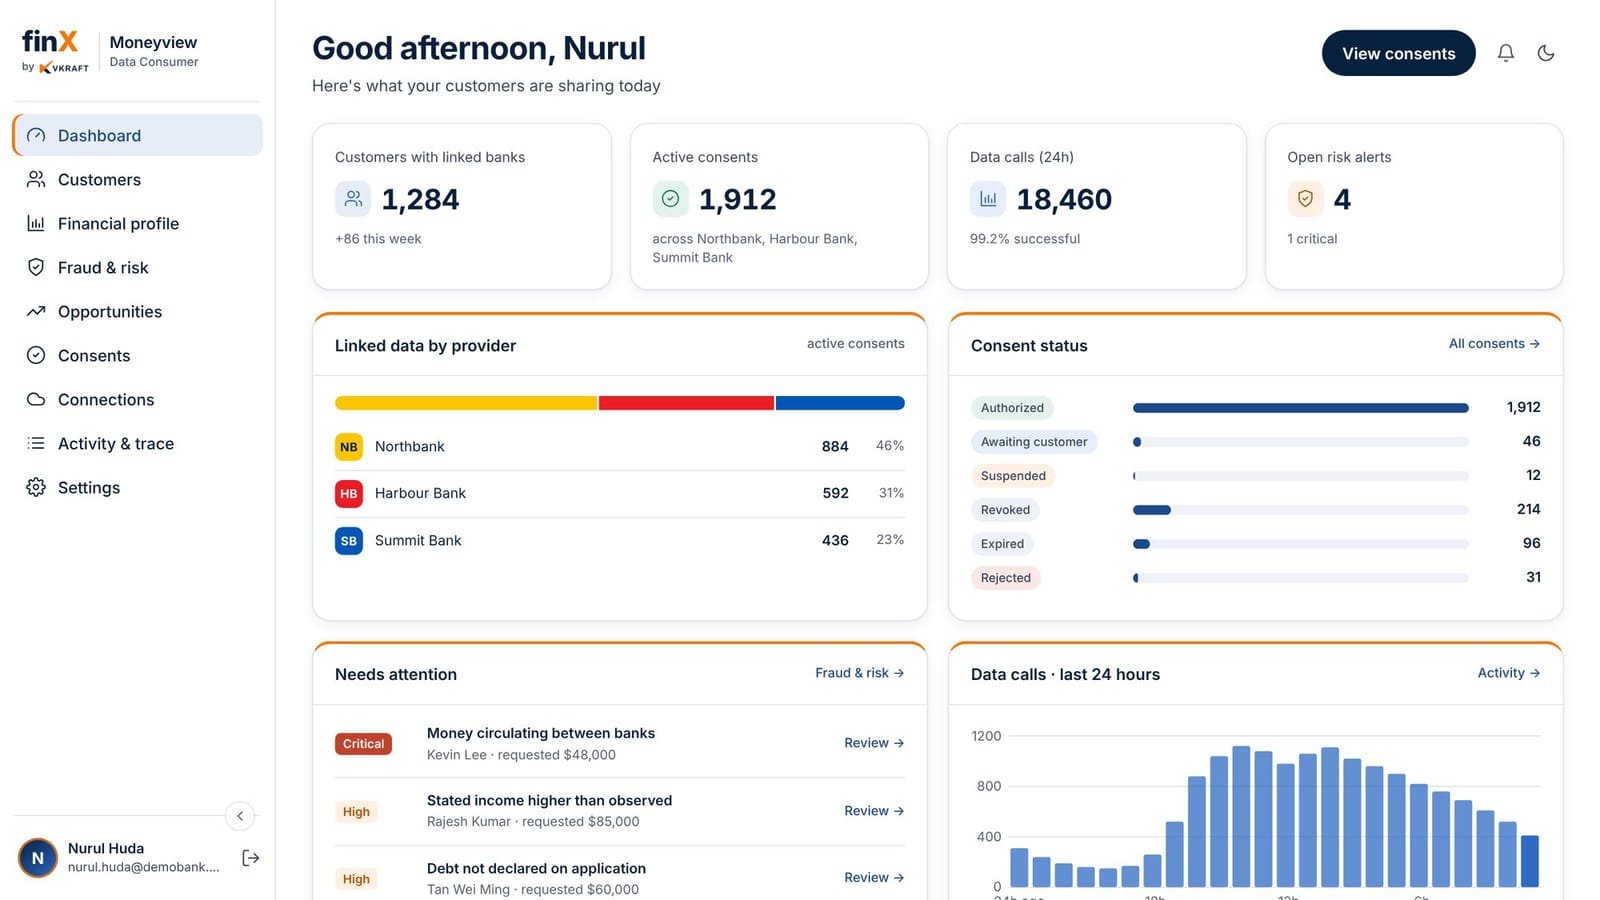
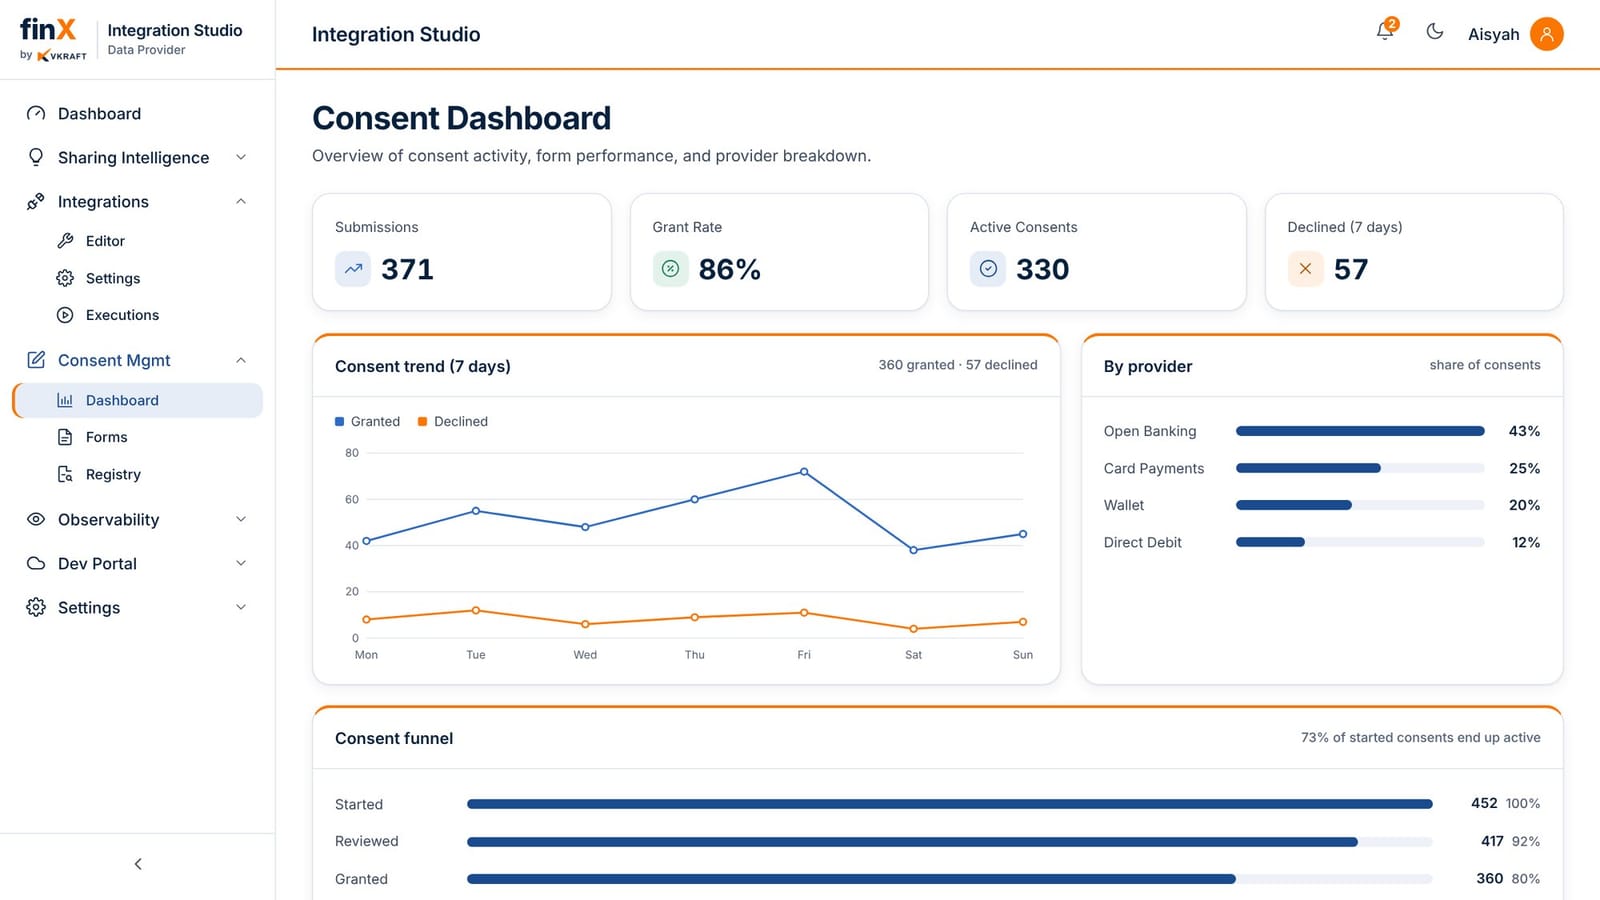
One platform, three views. The customer stays in control: they choose what to share and for how long, sign in only at their own bank, and can renew or revoke any consent at any time.
What you get
Take the full stack or individual modules, white-label ready, all configured from the same console.
Use cases
Every new use case runs on the same security, consent and audit foundation, so each release is faster than the last.
Share account and transaction data with partners on the customer's consent, FAPI-secured.
Reuses FAPI server · consent engine
Expose bank products to fintechs, super-apps and merchants through governed API channels.
Reuses Gateway · Integration Studio
Onboard, test and monitor partners in days, self-service from day one.
Reuses Sandbox · developer portal
The same FAPI-grade pipes for insurance, wealth, telco or any consent-driven integration.
Reuses Auth stack · zero-storage relay
One consent and audit fabric for inter-department and subsidiary data sharing.
Reuses Audit trail · registry
Consent, identity and audit as the base for the bank's digital stack.
Reuses Full platform
Questions
Consent, authorisation and the first read endpoints are the usual first milestone, in weeks rather than a multi-year programme. The pace mostly depends on how much of your core is already exposed through a supported interface.
Get started
Tell us about your institution and we will schedule a short technical walkthrough of finX.
Your path to a first release